China bans U.S., Israeli cybersecurity software, citing national security risks
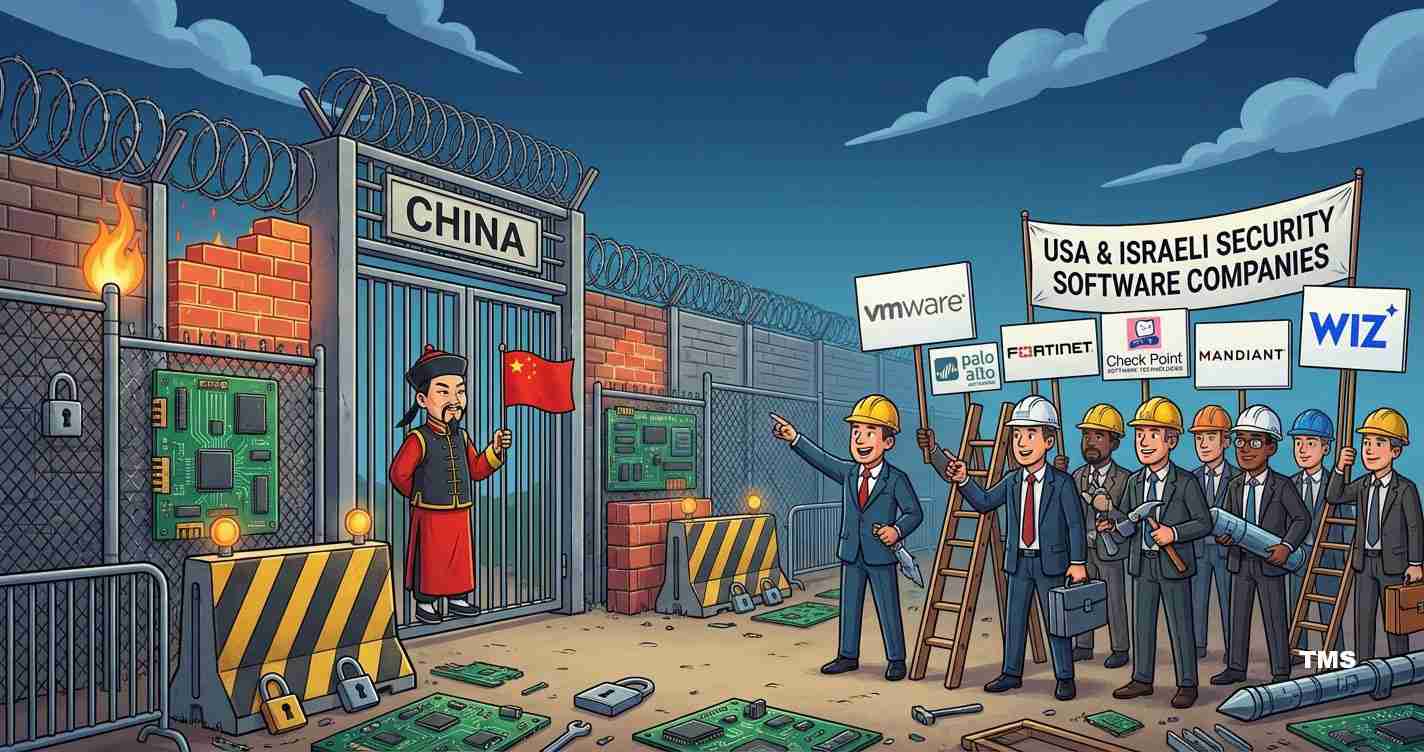
Chinese authorities have ordered domestic companies to stop using cybersecurity software from more than a dozen U.S. and Israeli firms, citing national security risks over potential data collection and overseas transmission as Beijing reduces reliance on Western technology.
- Regulators told firms to halt use of tools from multiple U.S. and Israeli vendors — sources cited by Fox Business, the Jerusalem Post and the Japan Times.
- Major vendors named include U.S. firms such as VMware (Broadcom), Palo Alto Networks, Fortinet, CrowdStrike and others — and Israeli firms including Check Point and CyberArk (Fox Business; Jerusalem Post).
- Officials cite risks that foreign-made software could collect or transmit sensitive data abroad, part of a broader push for domestic alternatives as U.S.-China tech competition intensifies (Japan Times).
What was ordered and who is affected
According to people briefed on the matter, Chinese regulators circulated notices in recent days asking many domestic companies to stop using cybersecurity products from a list of U.S. and Israeli vendors. The reports describe a broad set of tools — network monitoring, threat detection, cloud-security management — that often operate near or inside firms’ most sensitive systems.
Reported affected companies include U.S. vendors VMware (now owned by Broadcom), Palo Alto Networks, Fortinet, CrowdStrike, SentinelOne, Recorded Future, McAfee, Claroty, Rapid7, and Alphabet-owned Mandiant and Wiz. Israeli firms named include Check Point Software Technologies, CyberArk, Orca Security and Cato Networks. Imperva, now owned by French defense firm Thales, was also on the list (Fox Business; Jerusalem Post).
Why Chinese authorities say they acted
Officials warn that foreign-made cybersecurity software could gather confidential information and send it to servers outside China, creating a perceived national security risk. Regulators also argue that such products could be vulnerable to foreign hacking or manipulated to leak data — concerns that mirror long-standing Beijing anxieties about dependence on foreign technology (Fox Business; Jerusalem Post; Japan Times).
“The concern is not limited to espionage,” sources said, highlighting risks from both deliberate exfiltration and technical vulnerabilities.
Context: a wider tech rivalry and mixed signals
The directive comes as Beijing accelerates efforts to replace Western technologies with domestic alternatives amid a broader U.S.-China tech rivalry. Analysts describe this as part of a larger decoupling trend in which both sides seek greater control over technology supply chains (Japan Times; table.media).
The move also arrives amid mixed diplomatic and trade signals: Washington has tightened some export controls recently while allowing certain AI chip shipments under specific rules — a push-and-pull that underscores the complexity of tech policy between the two powers (Fox Business).
Diplomatic ties and timelines
Reports note the notices were issued after a Chinese envoy visited Israel earlier in the week, suggesting diplomatic discussions may have overlapped with decisions on tech and security. Reuters and other outlets could not independently confirm the full scope, and Chinese regulatory bodies did not respond to requests for comment, according to reporting cited by the Jerusalem Post.
Company responses and market fallout
As of the latest reports, the listed cybersecurity firms had not publicly responded. Market analysts warn such restrictions can reduce vendor revenue from China and push customers toward domestic or neutral third-country suppliers. For affected U.S. companies, lost market access could pressure sales growth and investor sentiment (Fox Business; Japan Times).
Implications for the United States
Economic impact
U.S. cybersecurity firms named could face lost revenue from Chinese customers, pressuring profit forecasts, stock prices and global sales strategies (Fox Business).
Political consequences
The action may harden U.S. political views that China is pursuing tech decoupling and could fuel calls for stronger export controls and tighter industry-government coordination (Japan Times; Fox Business).
Social and security effects
Businesses and NGOs operating in China may face higher cyber risks if forced to switch to unfamiliar domestic tools, potentially creating short-term defensive gaps that require careful management (Jerusalem Post; Japan Times).
Practical steps and next moves
Affected U.S. firms are expected to seek clarity from Chinese authorities and work with local customers to limit disruption. Washington may pursue private diplomatic channels while Congress and industry groups monitor supply-chain and cybersecurity funding needs. Investors and corporate boards will watch for earnings impacts and potential legal responses. Reporting to date is based on people familiar with the matter; independent confirmation remains limited (Jerusalem Post).
Reporting note
This article synthesizes recent coverage by Fox Business, the Jerusalem Post, the Japan Times and table.media, which cite people familiar with the directives. Chinese regulatory bodies did not respond to media queries at the time of reporting.