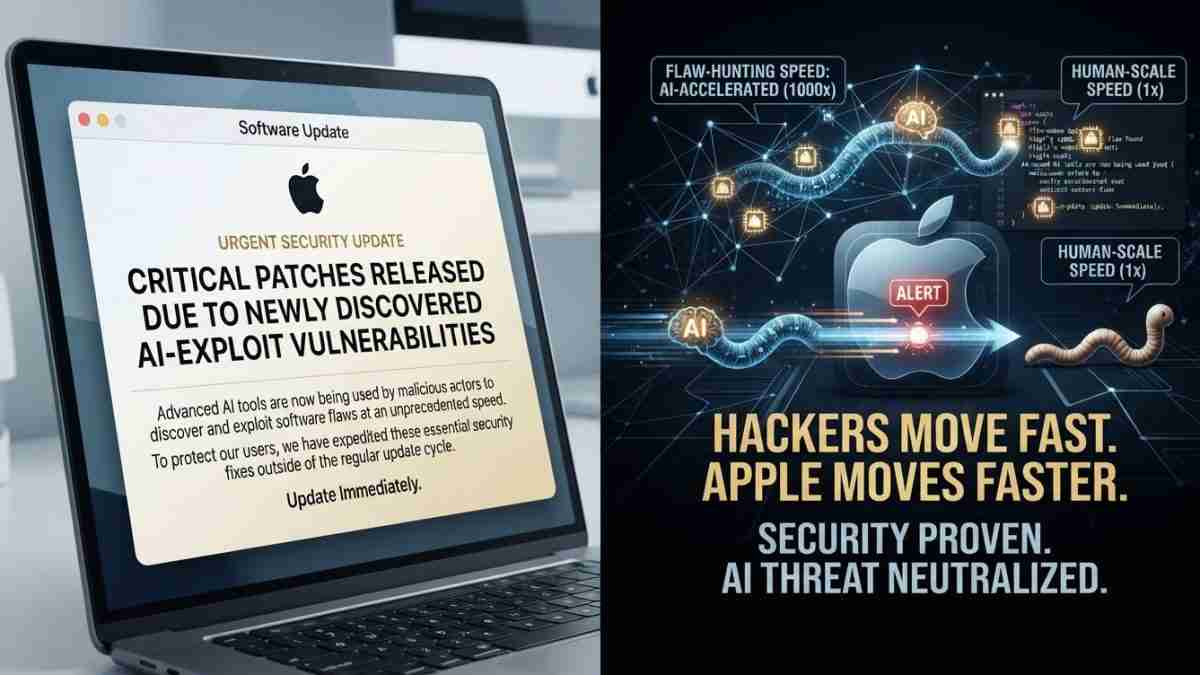
CUPERTINO, Calif., July 11 (San Francisco News Online) — Apple has released security updates for iPhone, iPad and Mac ahead of its normal software cycle, saying artificial intelligence is helping attackers move faster.
The company said the new fixes were shipped early because AI can speed the development of malicious hacking tools and shorten the time between when a flaw becomes public and when customers get a patch. Apple also said it had found no evidence that the newly fixed vulnerabilities had been exploited.
What changed?
Apple said it usually folds security fixes into broader software releases. This time, it moved the updates out early instead of waiting for the wider 26.6 release cycle.
The June 29 release included iOS 26.5.2, iPadOS 26.5.2 and macOS Tahoe 26.5.2. Apple said the fixes had first appeared in beta versions of iOS 26.6, iPadOS 26.6 and macOS Tahoe 26.6 before being pushed out sooner.
What kinds of bugs were fixed?
Apple’s update notes, as summarized in security coverage, pointed to problems in parts of the operating system and browser software. Those included the kernel, WebKit, WebRTC, libxslt and the IOGPUFamily graphics component.
The kernel is the core of an operating system. If something goes wrong there, the whole device can be affected. WebKit is the engine behind Safari and other apps that display web content. WebRTC is software used for real-time audio and video in browsers and apps.
Apple said some of the issues could have allowed app crashes, kernel memory corruption or leaks of sensitive kernel state. Other bugs in WebKit could have led to crashes, memory corruption, data leaks or sandbox escapes, while some WebRTC flaws could have caused crashes.
Why does AI matter here?
Apple’s explanation reflects a broader worry in cybersecurity: AI can help both defenders and attackers move faster. A recent warning from the Five Eyes intelligence alliance said frontier AI could reshape offensive and defensive cyber capabilities and shorten the time between finding a flaw and turning it into a working attack.
That matters because security teams often race to patch a flaw after it is disclosed. If attackers can automate more of the research and exploit-building process, the safe window for users gets smaller.
What does ‘no evidence of exploitation’ mean?
It means Apple had not seen signs, at the time of release, that attackers were already using these specific bugs in the wild. It does not mean the flaws were harmless. It means Apple was acting before it saw proof that the bugs had become active attacks.
Apple’s decision also suggests a shift in pace, not necessarily a permanent change in policy. Based on Apple’s statement, the company is reacting to a faster threat environment by moving selected security fixes out sooner when it can.
The bottom line
For users, the main point is simple: Apple is shipping security fixes earlier than usual because the company believes AI is making it easier for attackers to turn flaws into weapons more quickly. The update covers major parts of the iPhone, iPad and Mac software stack, and Apple says it found no sign the patched issues had already been abused.